industry: In the wake of Claude Code's source code leak, 5 actions
Anthropic's Claude Code AI agent source code, comprising 512,000 lines of TypeScript, was accidentally leaked, revealing critical architectural details, security validators, and unreleased features. This breach creates new attack paths and forces enterprise security leaders to take immediate actions to protect their AI-assisted development environments.
Enterprise security leaders are facing a critical new layer of vulnerability following the accidental leak of Anthropic's Claude Code AI agent source code. On March 31, 2026, version 2.1.88 of the @anthropic-ai/claude-code npm package inadvertently exposed 512,000 lines of unobfuscated TypeScript. This significant breach, quickly mirrored across GitHub, has revealed the complete architectural blueprint of the AI agent, including its permission model, security validators, and unreleased features, making exploitation cheaper and more practical for potential attackers.
The Breach Details and Initial Response
The exposed source map file, weighing 59.8 MB, laid bare 1,906 files of Anthropic's agentic harness. This harness, crucial for directing Claude's language model to use tools, manage files, and execute commands, now offers an unprecedented roadmap for competitors and malicious actors alike. Key revelations included a 46,000-line query engine managing context, 40+ tool schemas, and 2,500 lines detailing 23 sequential bash security validation checks.
Anthropic acknowledged the exposure as a human error in packaging, asserting no customer data or model weights were involved. However, their attempts to contain the spread via DMCA takedown requests on GitHub proved largely ineffective, with rewrites of Claude Code's functionality quickly going viral in other programming languages. The incident was compounded by the simultaneous availability of malicious axios npm packages, raising fears that some users may have inadvertently pulled both the exposed source and unrelated malware.
A "Systemic Signal" from Gartner
This incident marks the second leak for Anthropic in five days, following a CMS misconfiguration that exposed nearly 3,000 internal assets, including details of an unreleased model called Claude Mythos. Gartner's "First Take" analysis labeled these events a "systemic signal," urging organizations to re-evaluate their AI development tool vendors based on operational discipline, not just product capability. The firm also highlighted that Claude Code's 90% AI-generated nature, under current U.S. copyright law, means its leaked code carries diminished intellectual property protection — a new challenge for enterprises shipping AI-written production code.
New Attack Vectors Emerge
Security researchers have swiftly mapped three practical attack compositions now feasible due to the readable source. These include "context poisoning" through Claude Code's four-stage compaction pipeline, where malicious instructions embedded in project configuration files can be laundered into legitimate user directives. Another path involves "sandbox bypass" by exploiting differentials between the agent's three bash command parsers and early-allow decisions in security validators. The combination of context poisoning with validator gaps allows a cooperative agent to execute weaponized bash commands that appear legitimate.
Elia Zaitsev, CrowdStrike's CTO, stressed the critical importance of least privilege for agents. "Don't give an agent access to everything just because you're lazy," Zaitsev warned, emphasizing that an agent's power from broad access makes open-ended coding agents particularly dangerous. He noted that while an agent can be tricked, damage only occurs when it acts on those instructions—precisely what the leaked source facilitates.
Escalating Risks in AI-Assisted Development
The broader landscape of AI-assisted coding is already showing concerning trends. GitGuardian's 2026 report revealed Claude Code-assisted commits leaked secrets at a 3.2% rate, double the baseline for public GitHub commits. AI service credential leaks surged 81% year-over-year, with thousands of live credentials found in MCP configuration files. This data suggests AI's speed amplifies human workflow failures, rather than being a simple tool defect.
Gartner also noted Anthropic's rapid feature velocity, shipping over a dozen Claude Code releases in March alone. While introducing capabilities like autonomous permission delegation and remote code execution, this pace simultaneously widened the operational surface, making the subsequent leak more impactful. Merritt Baer, CSO at Enkrypt AI, added a layer of complexity, questioning who retains IP rights over derived artifacts like embeddings or reasoning traces when models are heavily AI-generated.
Immediate Actions for Security Leaders
Given these escalating risks, enterprise security leaders must act decisively. The following five actions are critical to mitigate immediate threats and enhance resilience:
- Audit CLAUDE.md and .claude/config.json in every cloned repository: Context poisoning through these files is a documented attack path with a readable implementation guide. Check Point Research found that developers inherently trust project configuration files and rarely apply the same scrutiny as application code during reviews.
- Treat MCP servers as untrusted dependencies: Pin versions, thoroughly vet before enabling, and continuously monitor for changes, leveraging the now-public interface contract revealed by the leak.
- Restrict broad bash permission rules and deploy pre-commit secret scanning: Narrowing agent permissions and scanning MCP configuration files are crucial to prevent credential exposure, which is heightened in AI-assisted workflows. GitGuardian reported that 24,008 unique secrets were found in MCP configuration files on public GitHub.
- Require SLAs, uptime history, and incident response documentation from AI coding agent vendors: Enterprises should demand operational maturity from vendors, architecting provider-independent integration boundaries to enable vendor switches within 30 days if necessary.
- Implement commit provenance verification for AI-assisted code: With the "Undercover Mode" module potentially stripping AI attribution from commits with no force-off option, regulated industries must enforce disclosure policies and verify the origin of code to maintain audit trails.
The Claude Code leak underscores that even non-novel security failures, like source map exposure, can have profound implications when targeting widely adopted, high-value AI infrastructure. With its full architectural blueprint now widely available, immediate and proactive defense measures are imperative.
FAQ
Q: What exactly was exposed in the Claude Code leak? A: The leak exposed 512,000 lines of unobfuscated TypeScript source code from Anthropic's Claude Code AI agent harness. This included the complete permission model, bash security validators, unreleased feature flags, and references to upcoming models.
Q: How does this leak impact enterprises using AI coding agents? A: It diminishes a layer of defense by providing a detailed blueprint for potential attackers to craft exploits, enabling new attack paths like context poisoning and sandbox bypass. It also raises questions about intellectual property protection for AI-generated code and highlights the need for increased operational discipline from AI tool vendors.
Q: What is the most immediate action security leaders should take?
A: Security leaders should immediately audit CLAUDE.md and .claude/config.json files in all cloned repositories, treating them as executable code rather than just metadata, due to the documented risk of context poisoning.
Related articles

Apple Unveils iPhone Duo: Pricey Foldable Sees Soaring Demand
Apple has officially entered the foldable smartphone arena with the long-anticipated launch of the iPhone Duo. Priced starting at a hefty $1,999, the device features a 5.4-inch outer display and a larger 7.6-inch inner

in-depth: Chicago-Area Cops Helped HSI Spy on Minnesota Anti-ICE
Chicago-area law enforcement, including local police and HSI agents, conducted undercover surveillance on Minnesota anti-ICE activists at an April 2, 2022, talk in Chicago. This operation was part of a federal conspiracy probe into 15 Minnesota activists facing felony charges related to immigration enforcement resistance. Civil liberties advocates have condemned the surveillance as a troubling intrusion into protected political activity.

Mark Wahlberg on using AI in film ‘the right way’ and being open to
Actor Mark Wahlberg believes AI has a place in filmmaking if used responsibly for enhancement, not script generation or actor replacement. At TechCrunch Disrupt, he expressed openness to an AI likeness carrying on his legacy, managed by his family, and emphasized storytelling.
Ars Technica's Rocket Report: Your Essential Space Industry Briefing
Quick Verdict Ars Technica's Rocket Report, presented by veteran space reporter Stephen Clark, offers an invaluable and meticulously organized weekly (or similar frequency, implied by "Edition 9.15") digest of the most
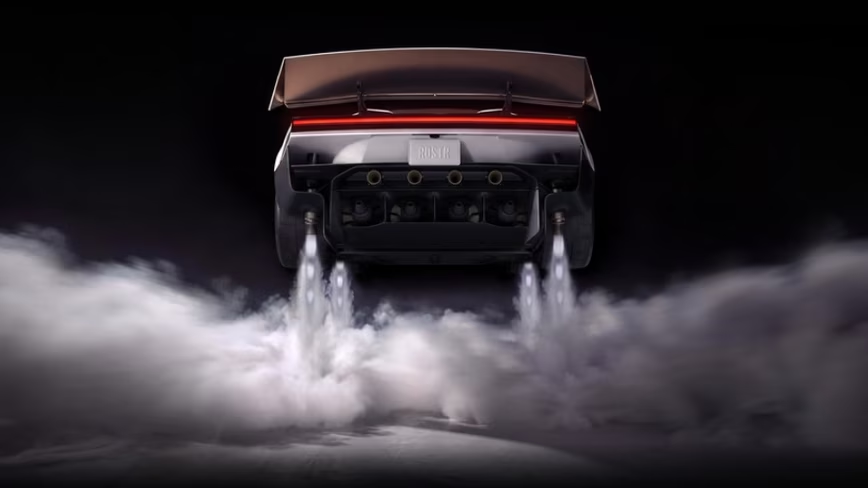
Tesla Unveils Thruster-Equipped Roadster, 2028 Production Targeted
Tesla has unveiled its second-generation Roadster, featuring cold-gas thrusters co-developed with SpaceX, enabling it to jump and flip. The electric sports car demonstrated 0-60mph in an astonishing 0.81 seconds, with production targeted for 2028. This highly anticipated reveal also serves as a key recruitment tool for Tesla's ambitious AI and robotics initiatives.

AI's Confidence vs. Formal Methods' Rigor: Design Flaws & Verification
While AI accelerates code generation, formal methods remain critical for ensuring system correctness. Languages like TLA+ and tools like Quint enable developers to model and verify system designs before coding, catching subtle flaws. Quint makes formal methods more accessible with developer-friendly syntax and executability. This approach is vital for verifying AI-generated code through trace validation and model-based testing, ensuring reliability against real-world data.