Google froze its open source bug bounty program due to a ‘significant
Google has frozen its open source bug bounty program until Q1 2027, effective October 1, 2026. The pause is due to a "significant rise" in invalid, AI-generated submissions overwhelming its security teams. This move highlights the growing challenge of AI "slop" in cybersecurity.

Google Halts Open Source Bug Bounty Program Amid Deluge of AI-Generated Reports
Google has temporarily suspended its Open Source Software Vulnerability Rewards Program (OSS VRP), effective October 1, 2026, citing an overwhelming influx of "automated submissions." The tech giant attributes this pause to a "significant rise" in reports generated by artificial intelligence, with the vast majority proving invalid or containing what engineers described as "hallucinations," effectively swamping the program's maintainers. This move leaves a critical security initiative on hold until at least the first quarter of 2027, when Google expects to provide an update on its future.
The Overwhelm of AI Slop
The decision follows earlier warnings from cybersecurity experts in 2025, who had predicted that the increasing prevalence of AI-generated content, often termed "AI slop," would pose a severe challenge to bug bounty programs. These platforms are designed to incentivize independent security researchers to discover and responsibly report software vulnerabilities, playing a crucial role in enhancing the security posture of open-source projects. Google's OSS VRP specifically focused on uncovering flaws within the company's extensive portfolio of open source software.
According to reports from Tom's Hardware, Google engineers and open source maintainers have been struggling to cope with the sheer volume of these AI-generated reports. The invalid submissions required significant human effort to triage and dismiss, diverting resources from addressing legitimate security concerns and ultimately making the program unsustainable in its current form. The integrity of the program was compromised by the noise, making it harder to identify genuine threats amidst the flood of low-quality reports.
In official posts on both its X account (@GoogleVRP) and the dedicated program website, Google explicitly stated: "This pause is due to a significant rise in automated submissions, the vast majority of which are not valid." This blunt assessment underscores the severity of the issue Google is confronting.
Implications for Security Research
For the time being, security researchers who previously contributed to the OSS VRP are directed to consider participating in Google's other active bug bounty programs. This shift means a temporary halt to dedicated rewards for open source vulnerabilities, potentially leaving some aspects of Google's extensive open source ecosystem more exposed in the short term. The incident underscores a growing problem in the cybersecurity landscape, where the promise of AI-driven efficiency in some areas is met with the challenge of AI-generated misinformation in others.
The pause highlights an emerging tension between the rapid proliferation of AI tools and established security practices. While AI can assist in vulnerability discovery, its uncritical application can also flood systems with noise, making it harder for human experts to identify genuine threats. Google's situation may serve as a critical case study for other organizations running similar bug bounty initiatives, forcing a reevaluation of how such programs can be safeguarded against the deluge of low-quality, automated submissions.
Google's commitment to providing an update in early 2027 suggests an internal reevaluation and potential restructuring of the program is underway. This could involve implementing more sophisticated filtering mechanisms, leveraging AI itself to screen submissions, or adjusting the program's scope and reward structure to better manage the evolving threat landscape. The long-term implications for open source security, both within Google and across the wider industry, depend heavily on the solution Google ultimately implements.
This incident serves as a stark reminder that even well-intentioned security initiatives can be overwhelmed by unintended consequences of new technologies. The move by Google also raises questions about the future of human-led security research in an increasingly automated world. Maintaining the delicate balance between incentivizing human expertise and embracing technological advancements will be crucial for the continued success of bug bounty programs worldwide.
FAQ
Q: Why did Google pause its open source bug bounty program?
A: Google paused its Open Source Software Vulnerability Rewards Program (OSS VRP) due to a "significant rise" in automated AI submissions. The company stated that the vast majority of these reports were invalid or contained "hallucinations," overwhelming its engineers and maintainers.
Q: When will Google's open source bug bounty program resume?
A: The program was frozen as of October 1, 2026. Google has committed to providing an update on its status in the first quarter of 2027, indicating a temporary suspension of at least several months.
Q: Can security researchers still report vulnerabilities to Google?
A: Yes, while the specific open source bug bounty program is paused, Google encourages participants to direct their efforts towards its other existing bug bounty programs, which remain operational.
Related articles
TCG Pocket Responds: A Much-Needed Pace Shift for Pokémon Fans
Pokémon TCG Pocket is rolling out a major update for its second anniversary, primarily addressing player concerns about overwhelming content releases by shifting to a six-week set schedule. This aims to curb player decline and improve overall engagement by giving trainers more time to collect and strategize. The update also adds new collection methods, improved deck-building features, and enhanced trading functionality.
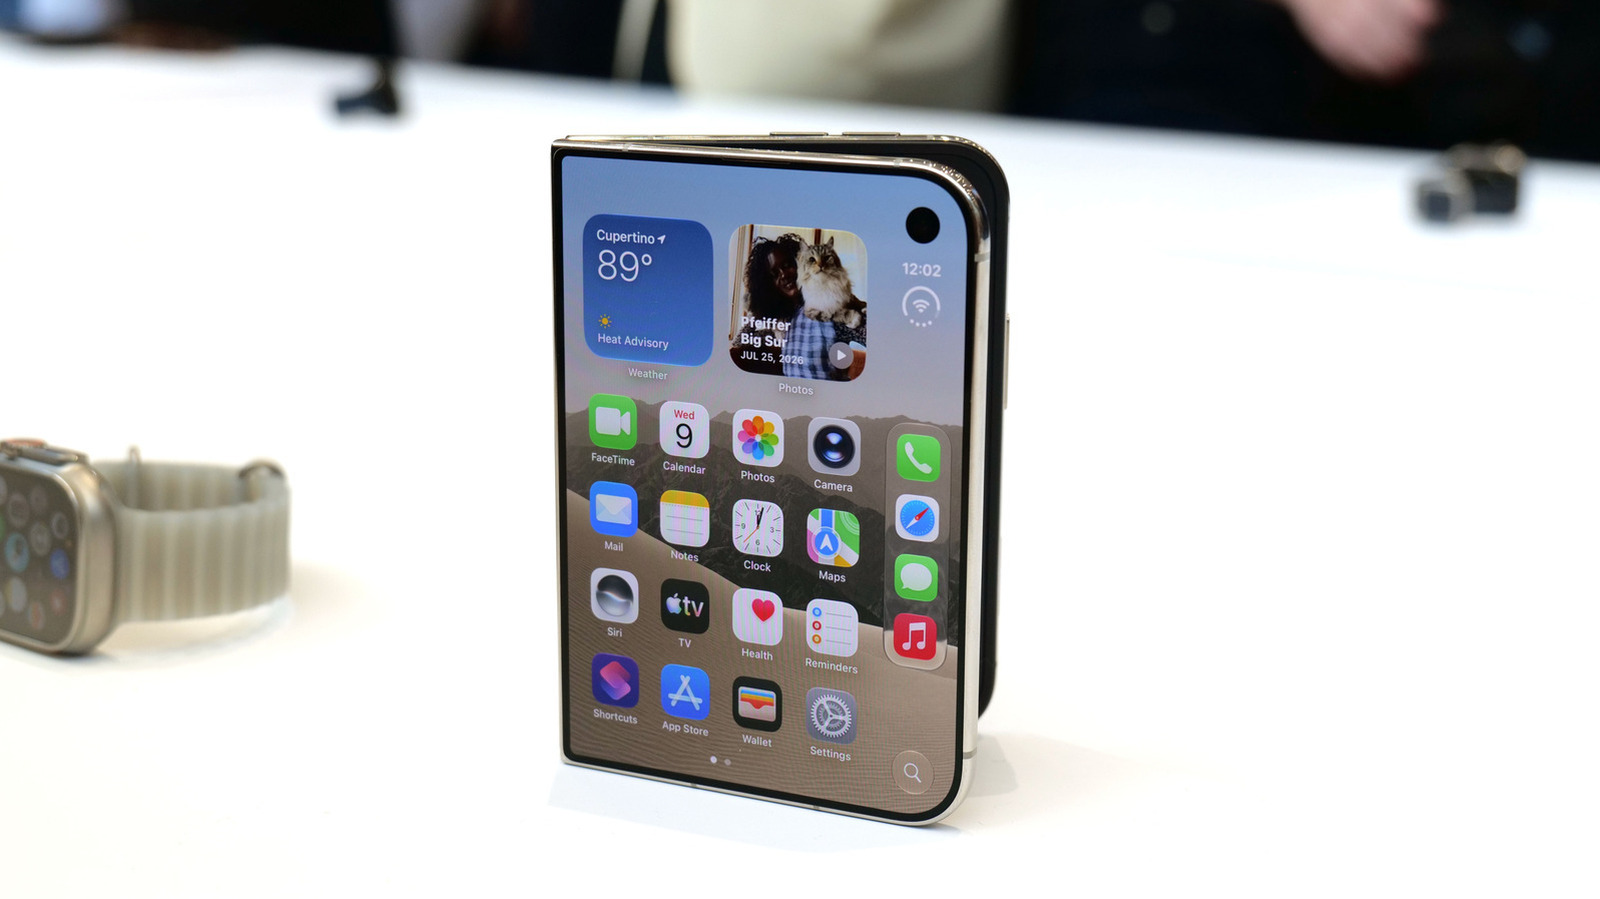
Apple iPhone Duo: A Daring Debut with Notable Compromises
Apple's highly anticipated iPhone Duo, priced at $2,000, has gone on pre-order. While hailed as "Apple's most exciting device in a decade" for its innovative foldable design and immersive display, it comes with significant drawbacks like the absence of FaceID and a premium camera.
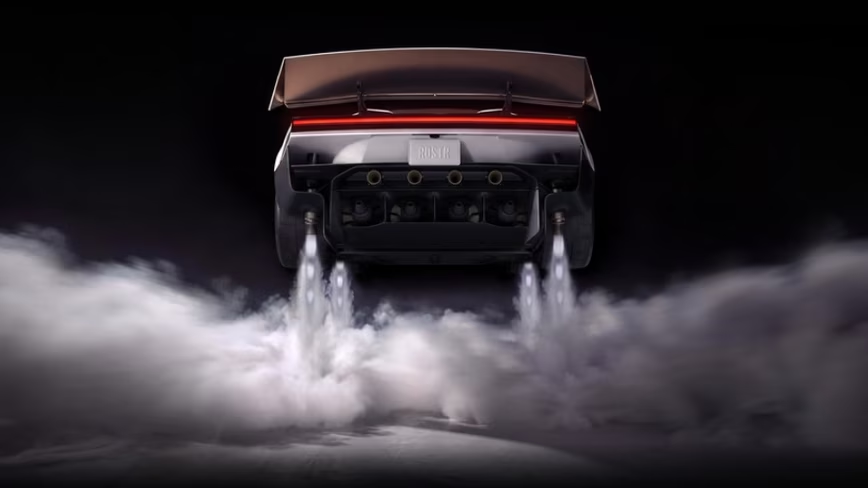
Tesla Unveils Thruster-Equipped Roadster, 2028 Production Targeted
Tesla has unveiled its second-generation Roadster, featuring cold-gas thrusters co-developed with SpaceX, enabling it to jump and flip. The electric sports car demonstrated 0-60mph in an astonishing 0.81 seconds, with production targeted for 2028. This highly anticipated reveal also serves as a key recruitment tool for Tesla's ambitious AI and robotics initiatives.

AI's Confidence vs. Formal Methods' Rigor: Design Flaws & Verification
While AI accelerates code generation, formal methods remain critical for ensuring system correctness. Languages like TLA+ and tools like Quint enable developers to model and verify system designs before coding, catching subtle flaws. Quint makes formal methods more accessible with developer-friendly syntax and executability. This approach is vital for verifying AI-generated code through trace validation and model-based testing, ensuring reliability against real-world data.
Amazon Prime Video Launches AI-Powered Prime 360 for NBA Coverage
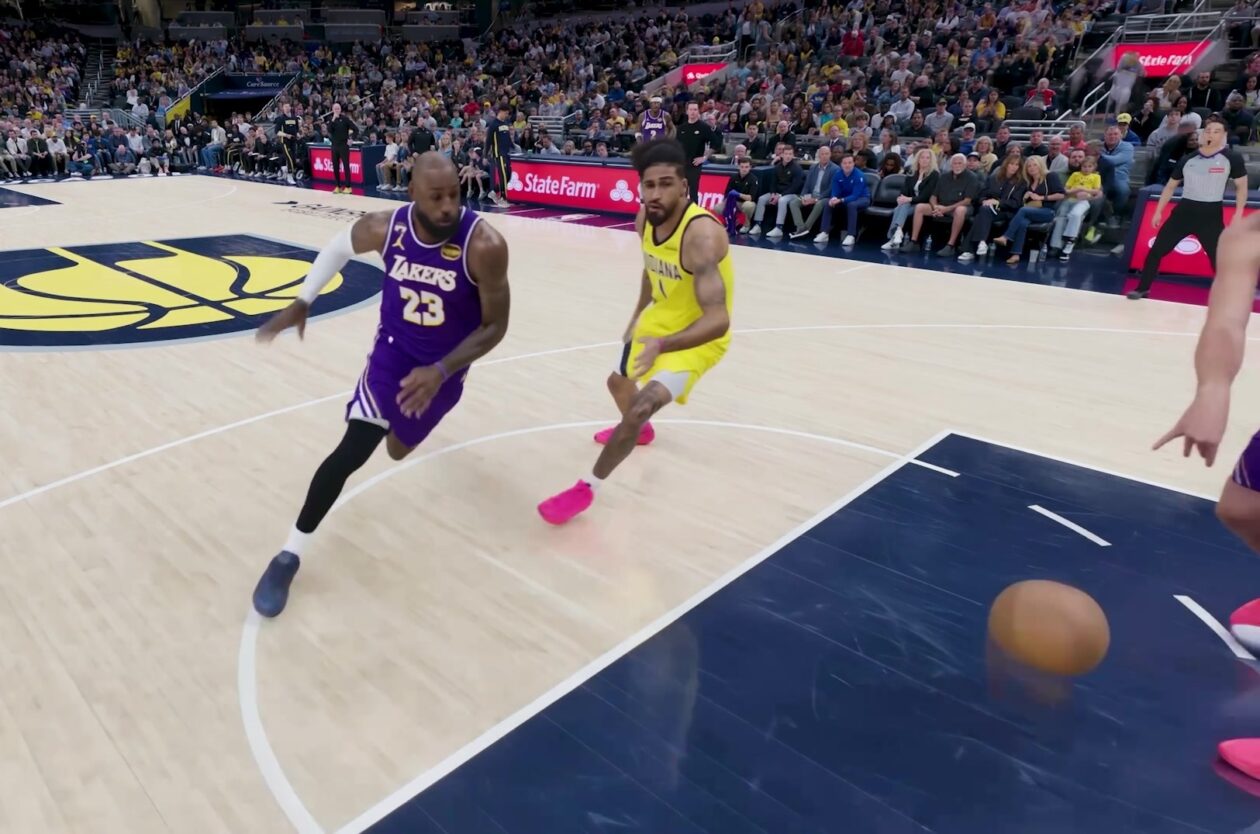
Amazon Prime Video is elevating its NBA coverage with the introduction of Prime 360, an AI-powered replay system offering immersive, 'fly through' views of the action. Kicking off its second season, Prime Video also adds Yahoo fantasy integration and gains exclusive Eastern Conference Finals rights, expanding its tech-driven sports broadcast. The new features aim to deliver a unique and interactive viewing experience for basketball fans.
regional: A two-person Seattle startup lands $1M to reinvent
Seattle startup TriMagnetix has secured $1 million to develop semiconductor chips that consume 800 times less energy and are radiation-resistant. The two-person company, leveraging nanomagnetic technology, is targeting space applications and data centers. With new funding and key partnerships, TriMagnetix aims for commercial sales within a year.